Skip to content
aizome
How aizome works

Identity First. Intent Always.

Making AI Agents Accountable Identity and control for every AI agent in your enterprise. No agent modification required. No rip and replace. Connect to your existing stack and start seeing results within hours.

Diagram of aizome’s identity-first, intent-always approach to enterprise AI agent governance

How aizome Makes Your Agents Accountable

From the first agent found to the last action logged, in under 90 seconds.

  • Every Agent Found, Scoped and Checked

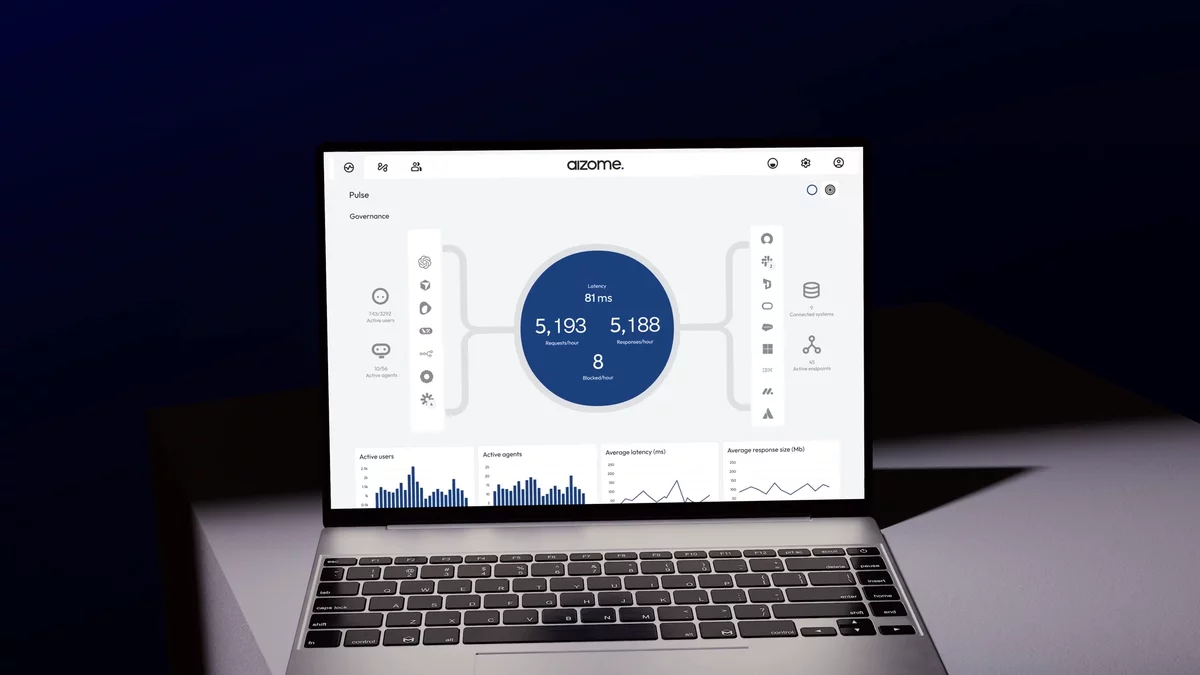
    Your workforce is building AI agents everywhere. aizome sits at the MCP gateway where every agent connects to your systems. It finds each agent in hours, not months, gives it a scoped identity validated before every action, and measures what it does against the intent it was given. Every interaction is logged and attributed, from identity to outcome.
  • Discovery

    See every AI agent across your stack, not one device at a time.

    aizome connects to the infrastructure you already run (IdP, MDM, EDR, CASB, firewalls, SASE, enterprise browsers, and email) to inventory every AI app, agent, integration, and user across your environment. No endpoint rollout required for baseline visibility. Cloud agents, SaaS AI, and unmanaged MCP servers surface in hours. Every discovered agent is scored by risk.

  • AI Gateway

    Every agent action authorized at runtime. Not by a service account. Not by a shared token.

    LLM Gateway

    Every prompt and response flows through aizome before it reaches the model. Authorization is evaluated per action, at the moment of execution, scoped to what the user can do and what the agent is allowed to do. Policy enforced pre- and post-tool-call. Set once. Enforced every time.

    MCP Gateway

    aizome federates your MCP servers (hosted, custom, or third-party) into a single governed endpoint. Credentials brokered inline, injected at execution, never exposed to agents or MCP clients. One URL. Every tool governed.

  • Intent

    Intent is a binding contract, not a setting.

    aizome synthesizes six inputs at runtime (user identity, agent baseline, system prompt, session context, current prompt, and the agent’s proposed plan) into an Execution Matrix that bounds authorized behavior across system, action type, and data class.

    Every action outside that matrix is blocked before execution. Drift, prompt injection, and goal hijacking stopped at the source, not detected after data moves.

What Happens When You Turn aizome On

From first connection to full governance, without a nine-month program.

Step 1

Step 1

Connect

Connect the systems you already run and the AI platforms your teams build with. One-time setup per system through an API key. No agent modification required. No rip and replace.

Step 2

Step 2

Discover

Within hours, aizome surfaces every AI platform, agent, integration, and user across your environment, including shadow agents and unmanaged MCP servers, by connecting to your existing IdP, MDM, EDR, CASB, and security stack. No endpoint deployment required for initial coverage.

Step 3

Step 3

Govern

Route agents through aizome’s LLM and MCP Gateways. Each agent inherits the user’s identity, scoped to least privilege, evaluated per action at runtime. Credentials are brokered and injected at execution, never held by the agent.

How It Works, in Detail

The questions technical teams ask first. Talk to us

See It in Action. Ask Anything

Thirty minutes. No slide deck. We will show you the product.

aizome enterprise AI agent governance platform