Skip to content
aizome
Comparison: aizome vs Onyx

Onyx watches what your agents do. aizome decides what they can reach.

Onyx monitors what an agent does with the access it already holds. aizome is where that access comes from: no credentials in the agent’s hands, a named employee behind every action, and the action checked before it runs.

  • What is aizome?

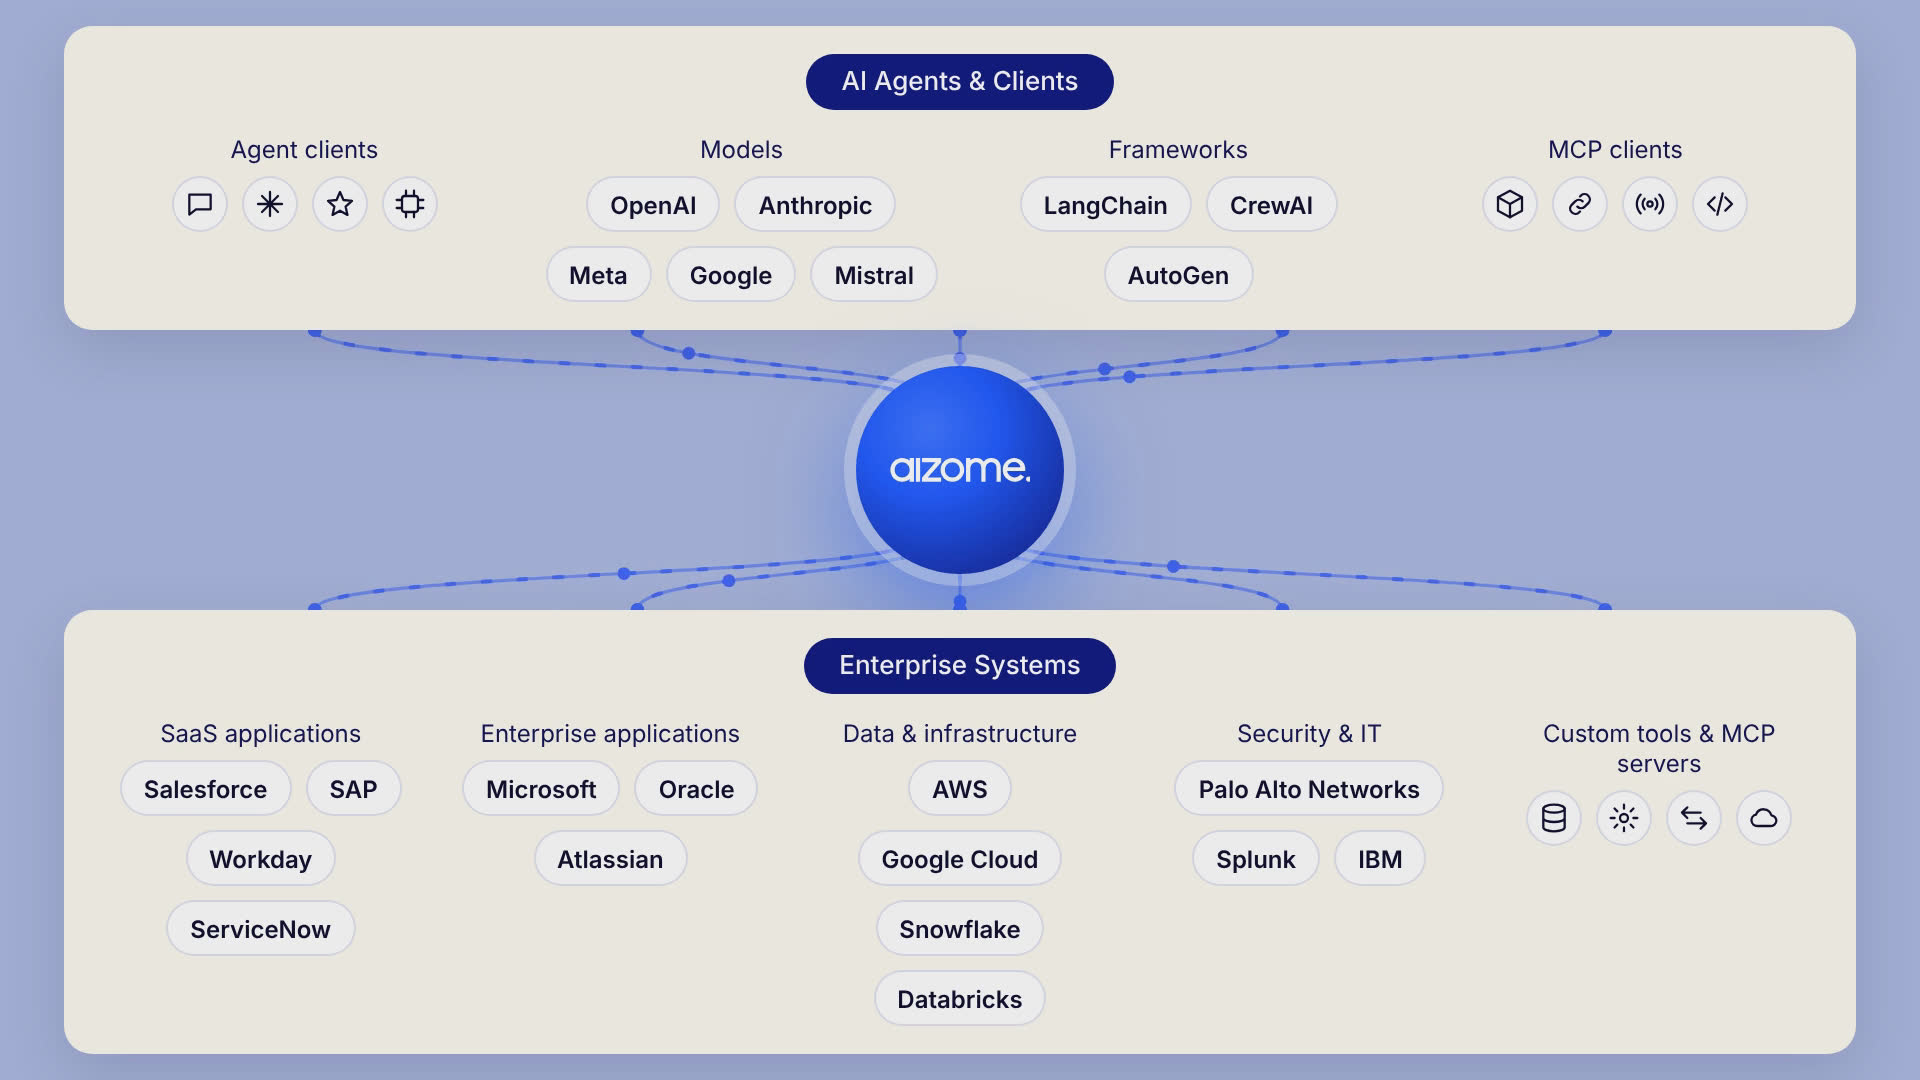
    aizome is the Identity-first AI Governance Platform. It sits as a single secure exchange (AI Gateway) between every AI agent your workforce deploys and every enterprise system those agents access, governing identity, enforcing intent, controlling cost, and making every agent accountable from day one.
  • What is Onyx?

    Onyx Security is a secure AI control plane. Its Guardian Agent is a supervisory AI that monitors each step of an agent’s reasoning and can block an action, narrow its scope, redirect it, or require human approval before it reaches a downstream system.

    Onyx security

Someone has to grant the access first

  • Onyx says it plainly: cloud-native controls govern identity, and Onyx governs what the agent decides to do with the access it has.

    That access came from somewhere else. In most enterprises it is a service account with broad standing permissions, created once and never narrowed. Onyx watches the agent make decisions inside that blast radius. It can stop a bad one, but the radius stays the size it was.

    aizome is where the access comes from. The agent holds no credential. It inherits what the employee behind it is already entitled to, and nothing more. The blast radius is one person’s job instead of one service account’s permissions.

Where each layer acts

The word ONYX.(Onyx)aizome
EnforcementInline proxy for MCP traffic, plus Edge proxies for workloadsThe inline path itself, between every agent and every system
Agent DiscoveryNot offered. Agents are registered and configuredEvery agent connecting to an enterprise system: local, SaaS, containerized, MCP
IdentityBlended identity. Agent attested cryptographically, bound to the user through your IdPThe target system sees a named employee, through your IdP
EntitlementPolicy decides what the blended identity may reachEvaluates the access behind the tool before the call executes
IntentNot offered. Policies evaluate identity, resource, time, geo, and riskEvery action checked against declared purpose before execution
CostOutside the modelPer-session token limits, cost drift detection
Human in the loopNot documented for agent flowsApproval required before destructive actions execute
EU AI ActAccess logging supports SOC 2, HIPAA, PCI controlsArticles 9, 12, 13, 14, 26

What aizome adds at the exchange

The agent never holds the credential

Access is brokered per call. There is no standing credential to over-scope, leak, or inherit.

The ceiling is a real person

Six-stage SAML impersonation means the target system sees a named employee, so the agent cannot exceed what that person can already do.

Reach beyond the AI platforms

Onyx governs through hooks into Anthropic, OpenAI, Bedrock, Copilot Studio, and Gemini. aizome connects agents to your core, your ERP, and systems with no modern API, where no platform hook exists.

Frequently asked questions

See every agent and what it is reaching for.

Thirty minutes, your environment. We will show you the agents nobody registered.

aizome enterprise AI agent governance platform