Skip to content
aizome
Comparison: aizome vs Noma Security

Watching isn’t governing.

Noma Security shows you the risk and leaves the work to your team. aizome puts a guardian agent and an intent engine in the path of every agent, so risky actions are stopped before they run, spend stays capped, and compliance evidence builds itself. A policy is only as good as the path it runs on.

  • What is aizome?

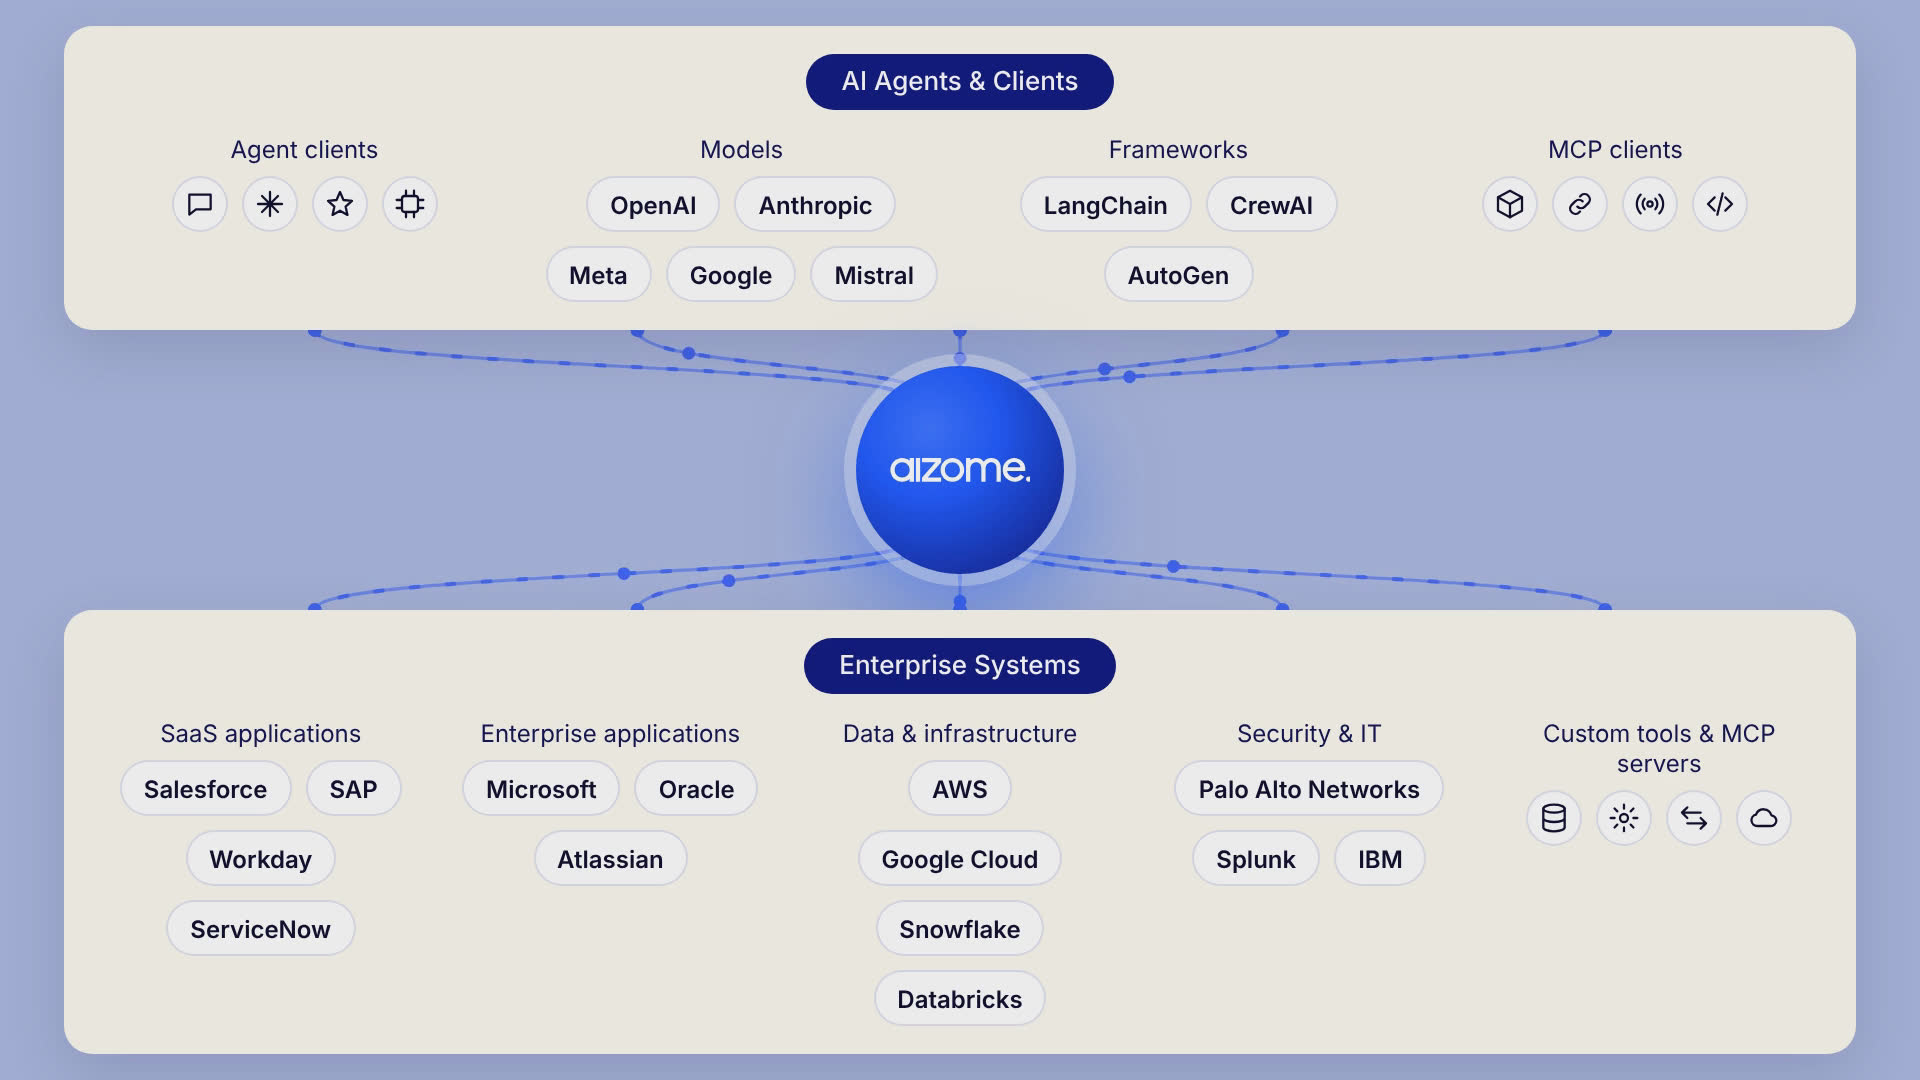
    aizome is the Identity-first AI Governance Platform. It sits as a single secure exchange (AI Gateway) between every AI agent your workforce deploys and every enterprise system those agents access, governing identity, enforcing intent, controlling cost, and making every agent accountable from day one.
  • What is Noma Security?

    Noma Security is an AI security platform covering agent discovery, posture management, red teaming, and runtime detection. It inventories agents, MCP servers, and models across endpoint, SaaS, and in-house environments, and enforces policy through the gateways, EDR, MDM, and agent hooks you already run.

    Diagram contrasting Noma Security and aizome’s 4-step security processes. Noma Security requires customer team involvement for 3 steps, while aizome fully automates all steps.

Finding the risk is not the same as stopping it.

Noma knows which agents exist and when their behavior looks wrong. Stopping an action takes a control point in the path, and Noma’s own documentation describes enforcement as running through the gateways, EDR, and MDM you already have. Where one exists, the policy lands. Where none does, there is a policy and no way to apply it, and your team is left to do the work. aizome is that control point. Agents connect through it, so identity, intent, and cost are checked before the action runs.

Where each layer acts

Noma Security(Noma Security)aizome
Who does the workFindings and alerts go to your team to triage and tuneA guardian agent acts, and policy is applied without a ticket
EnforcementRuns through your existing gateways, EDR, MDM, and agent hooksThe inline path between every agent and every system
IntentDetects injection, leakage, and tool poisoningChecks every action against its declared purpose before it runs
CostNo cost controls in public documentationPer-session token limits, spend caps, and cost drift detection
ComplianceMaps frameworks to findingsBuilds evidence as agents run: NIST, EU AI Act Articles 9, 12, 13, 14, 26
Human in the loopDetectors can monitor, alert, block, or maskApproval required before destructive actions run
IdentityPolicies can reference the human an agent is attributed toThe target system sees a named employee, through your IdP
EntitlementGoverns which tools an agent may callEvaluates the access behind the tool before the call executes

What aizome adds at the exchange

Every action has a named owner

Agents hold no credentials of their own. Each action is bound to a named employee through the identity provider you already run.

Intent checked before the call runs

Every action is compared with the purpose the agent declared, before it executes.

Access evaluated behind the tool

aizome evaluates what a tool can reach in the system it connects to, not only whether the agent may call it.

Frequently asked questions

See every agent and what it is reaching for.

Thirty minutes, your environment. We will show you the agents nobody registered.

aizome enterprise AI agent governance platform