Skip to content
aizome
Comparison: aizome vs Aembit

Aembit controls the credential. aizome governs the action.

Aembit decides whether an agent may reach a resource. aizome decides whether what it is doing with that access is still its job.

  • What is aizome?

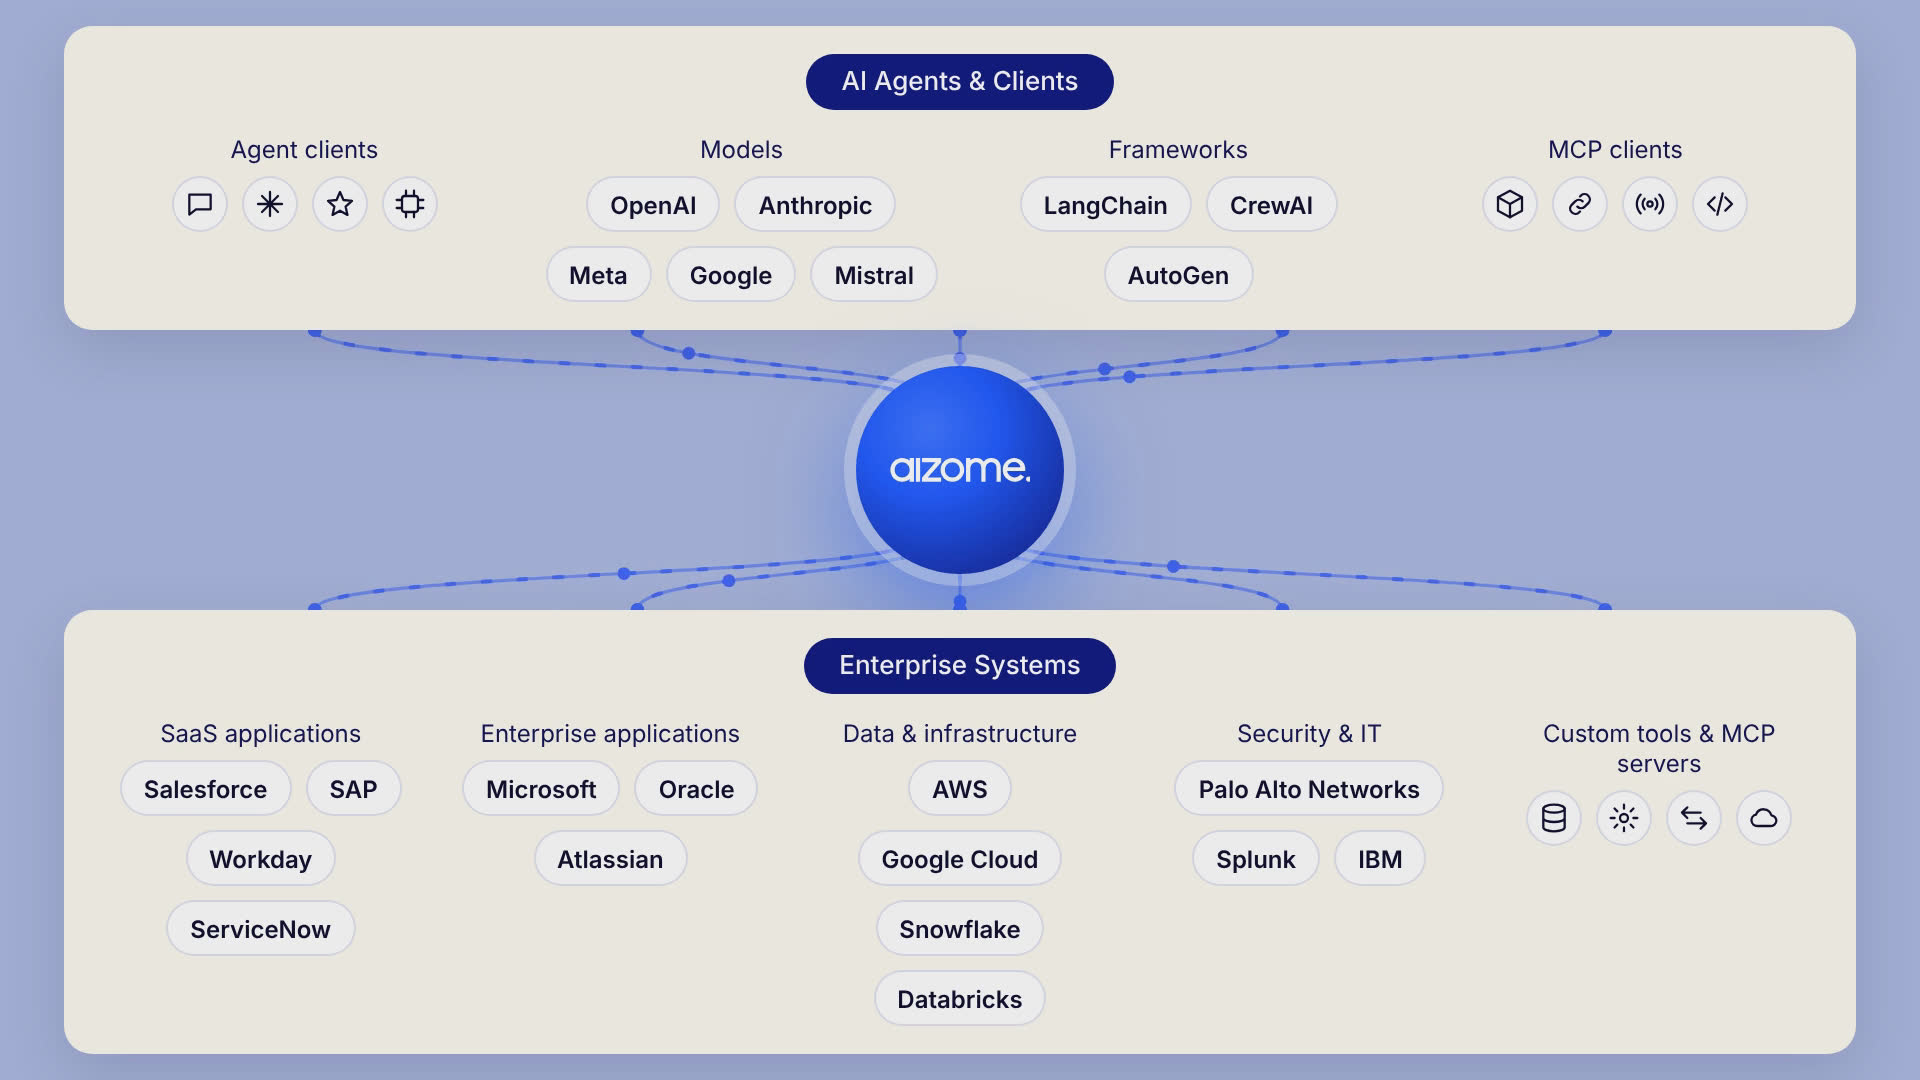
    aizome is the Enterprise AI Agent Control Platform. It sits as a single secured exchange between every AI agent your workforce deploys and every enterprise system those agents access, governing identity, enforcing intent, and making every agent accountable from day one.
  • What is Aembit?

    Aembit is a workload identity and access management platform extended to AI agents. Its blended identity model evaluates the human user and the agent’s workload identity in a single policy decision, and its MCP Identity Gateway proxies agent traffic so the agent never holds a credential, exchanging tokens and injecting per-user credentials at runtime.

    Diagram illustrating Aembit providing AI agent access and aizome enforcing policies throughout the agent’s execution, including tool calls and content reading.

Access is a precondition, not a control

  • With Aembit, the agent is verified, the user authenticates through your identity provider, policy checks both, and the credential never reaches the agent. It answers one question well: may this user, with this agent, reach this resource?

    That question is settled before the agent does anything. Once access is granted, everything it permits is permitted. An agent redirected by a document it read, or drifting from the task it was given, is still inside a decision that was made correctly.

    aizome answers the next question. Every action is checked against the purpose the agent was given, as it runs.

Where each layer acts

Aembit logo, featuring a red stylized ‘A’ symbol and the word ‘Aembit’ in red text.(Aembit)aizome
EnforcementInline proxy for MCP traffic, plus Edge proxies for workloadsThe inline path itself, between every agent and every system
Agent DiscoveryNot offered. Agents are registered and configuredEvery agent connecting to an enterprise system: local, SaaS, containerized, MCP
IdentityBlended identity. Agent attested cryptographically, bound to the user through your IdPThe target system sees a named employee, through your IdP
EntitlementPolicy decides what the blended identity may reachEvaluates the access behind the tool before the call executes
IntentNot offered. Policies evaluate identity, resource, time, geo, and riskEvery action checked against declared purpose before execution
CostOutside the modelPer-session token limits, cost drift detection
Human in the loopNot documented for agent flowsApproval required before destructive actions execute
EU AI ActAccess logging supports SOC 2, HIPAA, PCI controlsArticles 9, 12, 13, 14, 26

What aizome adds at the exchange

Every action has a named owner

Agents hold no credentials of their own. Each action is bound to a named employee through the identity provider you already run.

Intent checked before the call runs

Every action is compared with the purpose the agent declared, before it executes.

Access evaluated behind the tool

aizome evaluates what a tool can reach in the system it connects to, not only whether the agent may call it.

Frequently asked questions

See every agent and what it is reaching for.

Thirty minutes, your environment. We will show you the agents nobody registered.

aizome enterprise AI agent governance platform